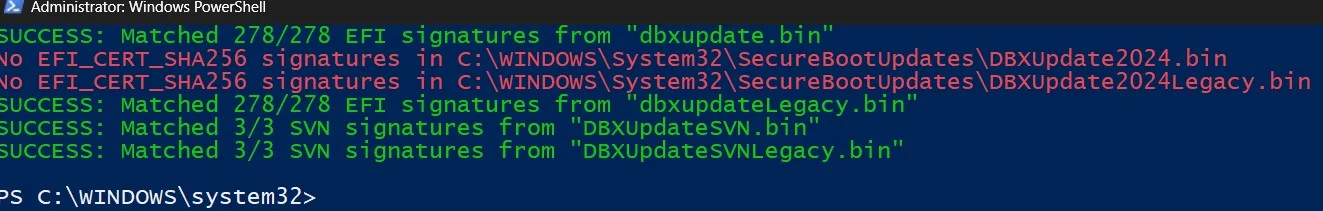
. Why did they bother renaming the files?
You should be able to run "Update_UEFI-CA2023.ps1 -Revoke -SkuSiPolicy", and it should force SVN 8 and a newer SkuSiPolicy.
PS C:\SecureBoot-CA-2023-Updates> powershell -nop -ep bypass -f .\Check_UEFI-CA2023.ps1 -Verbose -Audit
Windows 11 25H2 (26200.8246)
Secure Boot: ON
Virtualization Based Security: ON
BitLocker on (C:) OFF
BIOS Firmware
-------------
LENOVO 20VD
Version: F8CN59WW(V2.22)
Date: 2024-06-14
Factory Default UEFI PK Cert
----------------------------
Ideapad Products
UEFI PK Cert
------------
Ideapad Products
Factory Default UEFI KEK Certs
------------------------------
Microsoft Corporation KEK CA 2011
UEFI KEK Certs
--------------
Microsoft Corporation KEK CA 2011
Microsoft Corporation KEK 2K CA 2023
Factory Default UEFI DB Certs
-----------------------------
Microsoft Corporation UEFI CA 2011
Microsoft Windows Production PCA 2011
Compal_Test
F8V350-ITL
UEFI DB Certs
-------------
Microsoft Corporation UEFI CA 2011
Microsoft Windows Production PCA 2011
Microsoft Option ROM UEFI CA 2023
Microsoft UEFI CA 2023
Windows UEFI CA 2023
Compal_Test
F8V350-ITL
Factory Default UEFI DBX Certs
------------------------------
(NONE)
EFI_CERT_SHA256_GUID Signatures: 33
UEFI DBX Certs
--------------
Microsoft Windows Production PCA 2011
Windows BootMgr SVN 8.0
EFI_CERT_SHA256_GUID Signatures: 439
EFI Files
---------
Windows Boot Manager [Windows UEFI CA 2023] is ALLOWED.
\\.\HarddiskVolume1\EFI\Microsoft\Boot\bootmgfw.efi
File Version: 28000.322, SVN 8.0
Registry: WindowsUEFICA2023Capable = 2
[Windows UEFI CA 2023] in UEFI DB, and Windows starting from CA 2023 Boot Manager.
SkuSiPolicy.p7b is CURRENT.
\\.\HarddiskVolume1\EFI\Microsoft\Boot\SkuSiPolicy.p7b
Version: 3.0.0.14
AUDIT REPORT
============
STATUS REPORT
-------------
Registry: UEFICA2023Status = Updated
SUCCESS: UPDATES ARE FINISHED. UEFI CA 2023 certs are present, PCA 2011 cert is revoked.
All good now?