Modern Standby/Hibernate Cause a Crash into Shutdown Each Time


pacificSurf

Well-known member
Member
Local time
10:17 PM
Posts
181
OS
windwos 11 pro
2025 Surface Laptop 7. Windows 11 Pro, 25H2
OS build 26200.9711. Windows Feature Experience Pack 1000.26100.372.0
Notes: I have Bitlocker with Pre-Boot Pin Enabled. Sleep Study could not be attached because forum doesnt allow HTML file, I've included it in a Google Folder and the Energy Report and Event Viewer List and V2 Log Collector Results here--> ElevenForums - Google Drive

Issue:
Both Sleep (Modern Standby) and Hibernate, lead to the laptop shutting down, Error 41, upon attempting to wake it back up. Happens within a minute or so of putting it to Modern Standby or hibernate. Battery is at 50% to 80% at all times. Not a battery drain issue. There is no BSOD.

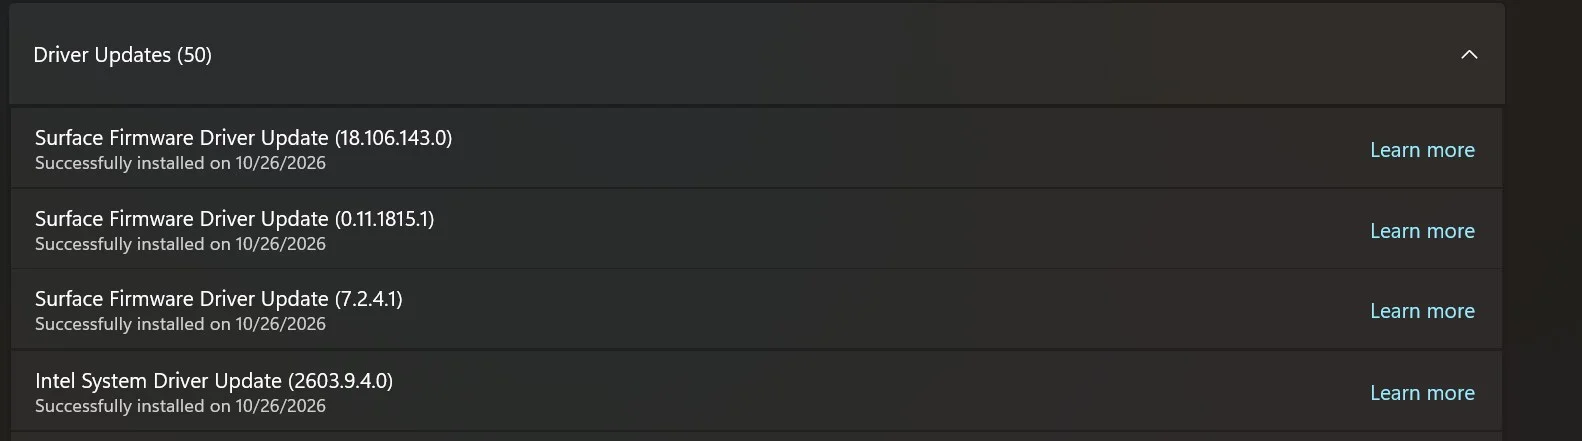
May be a coincidence, but I believe this *may have started after these recent windows and Surface Firmware updates below. I have not changed anything else recently:
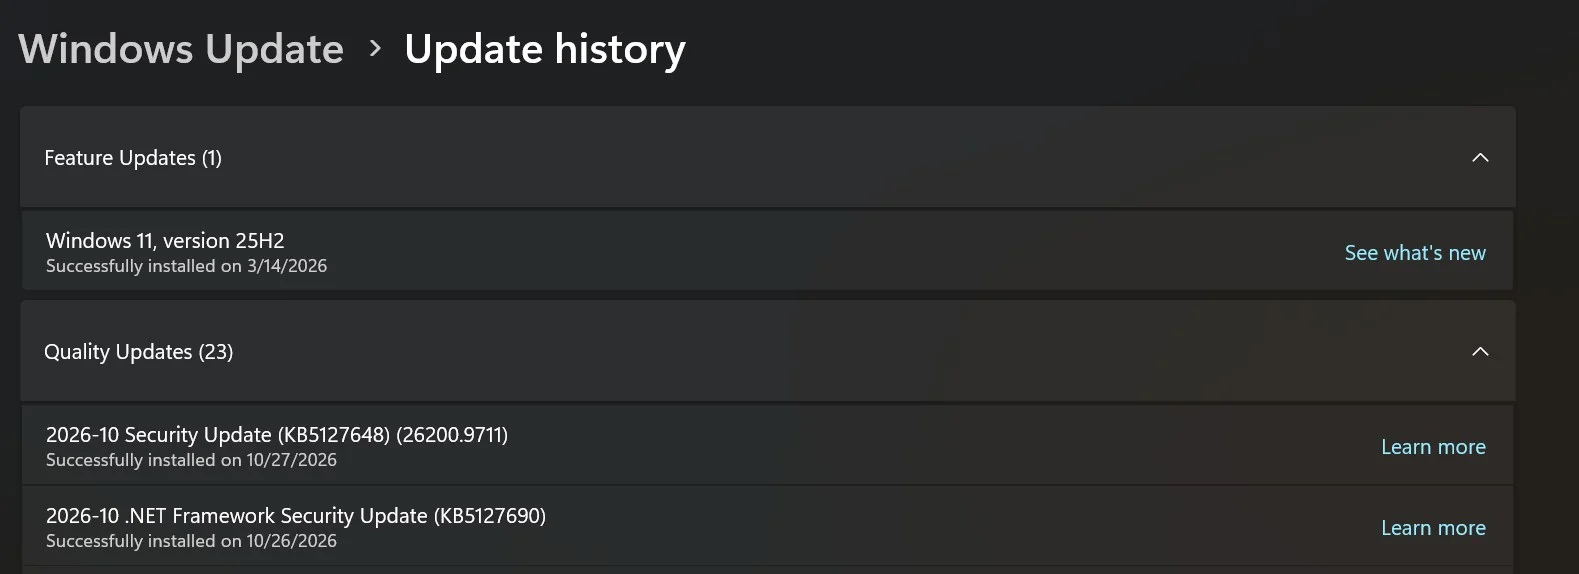
recent windows updates.webp
k9QSyjmmn7.webp


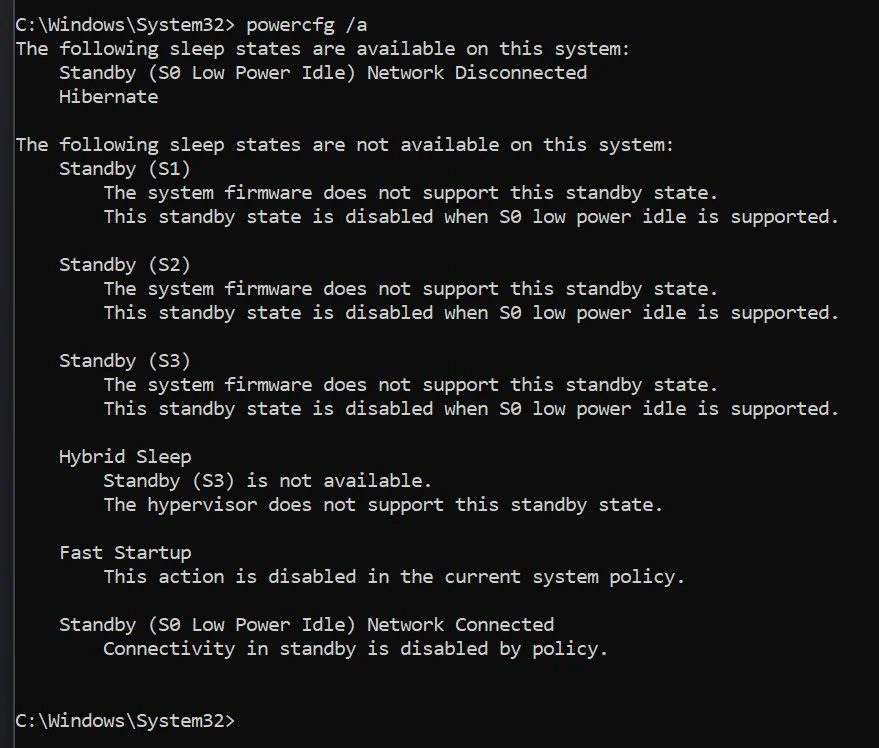
My available sleep states:
Sleep states.webp


My power options, these have never changed, so shouldnt be related. Hibernate is 2304 minutes because I didnt want it transitioning from sleep to Hibernate. These settings have existed like this for over a year. Network connectivity disabled. Not a battery drain issue.
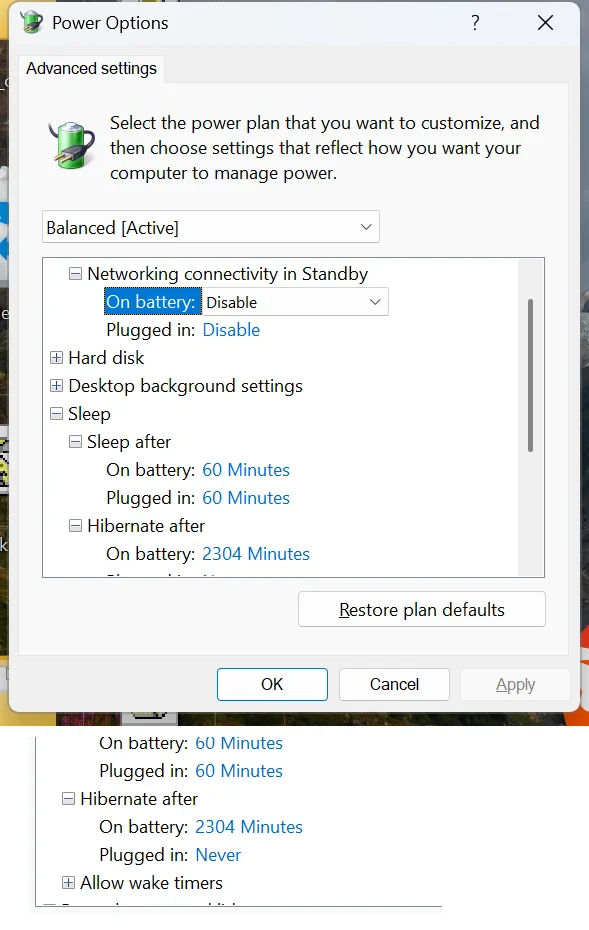
poweroptions.webp


Each time I wake it back up (From now a shutdown), I find a 41 error in event viewer:
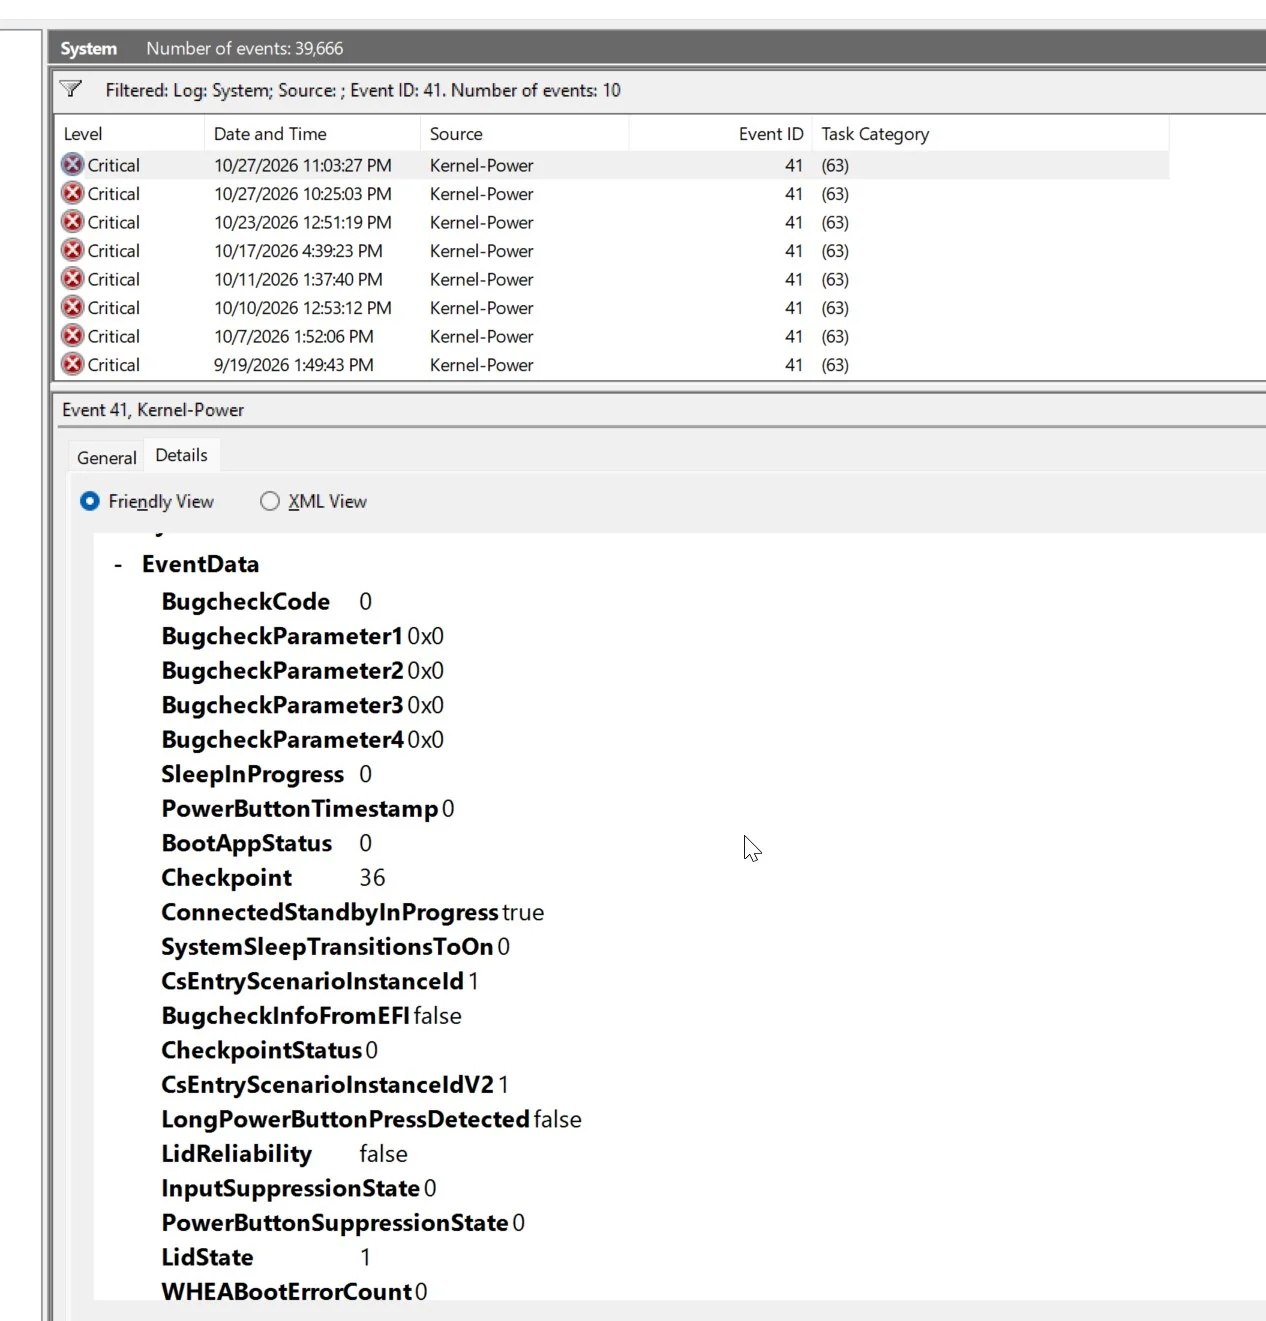
41 details section.webp


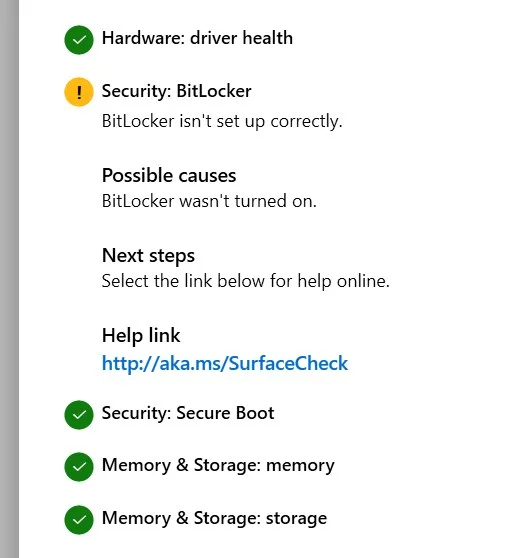
I ran Surface Diagnostic Toolkit, seems to lead to a Bitlocker possibility issue? But its resolutions (bitlocker protector check tool) does nothing:
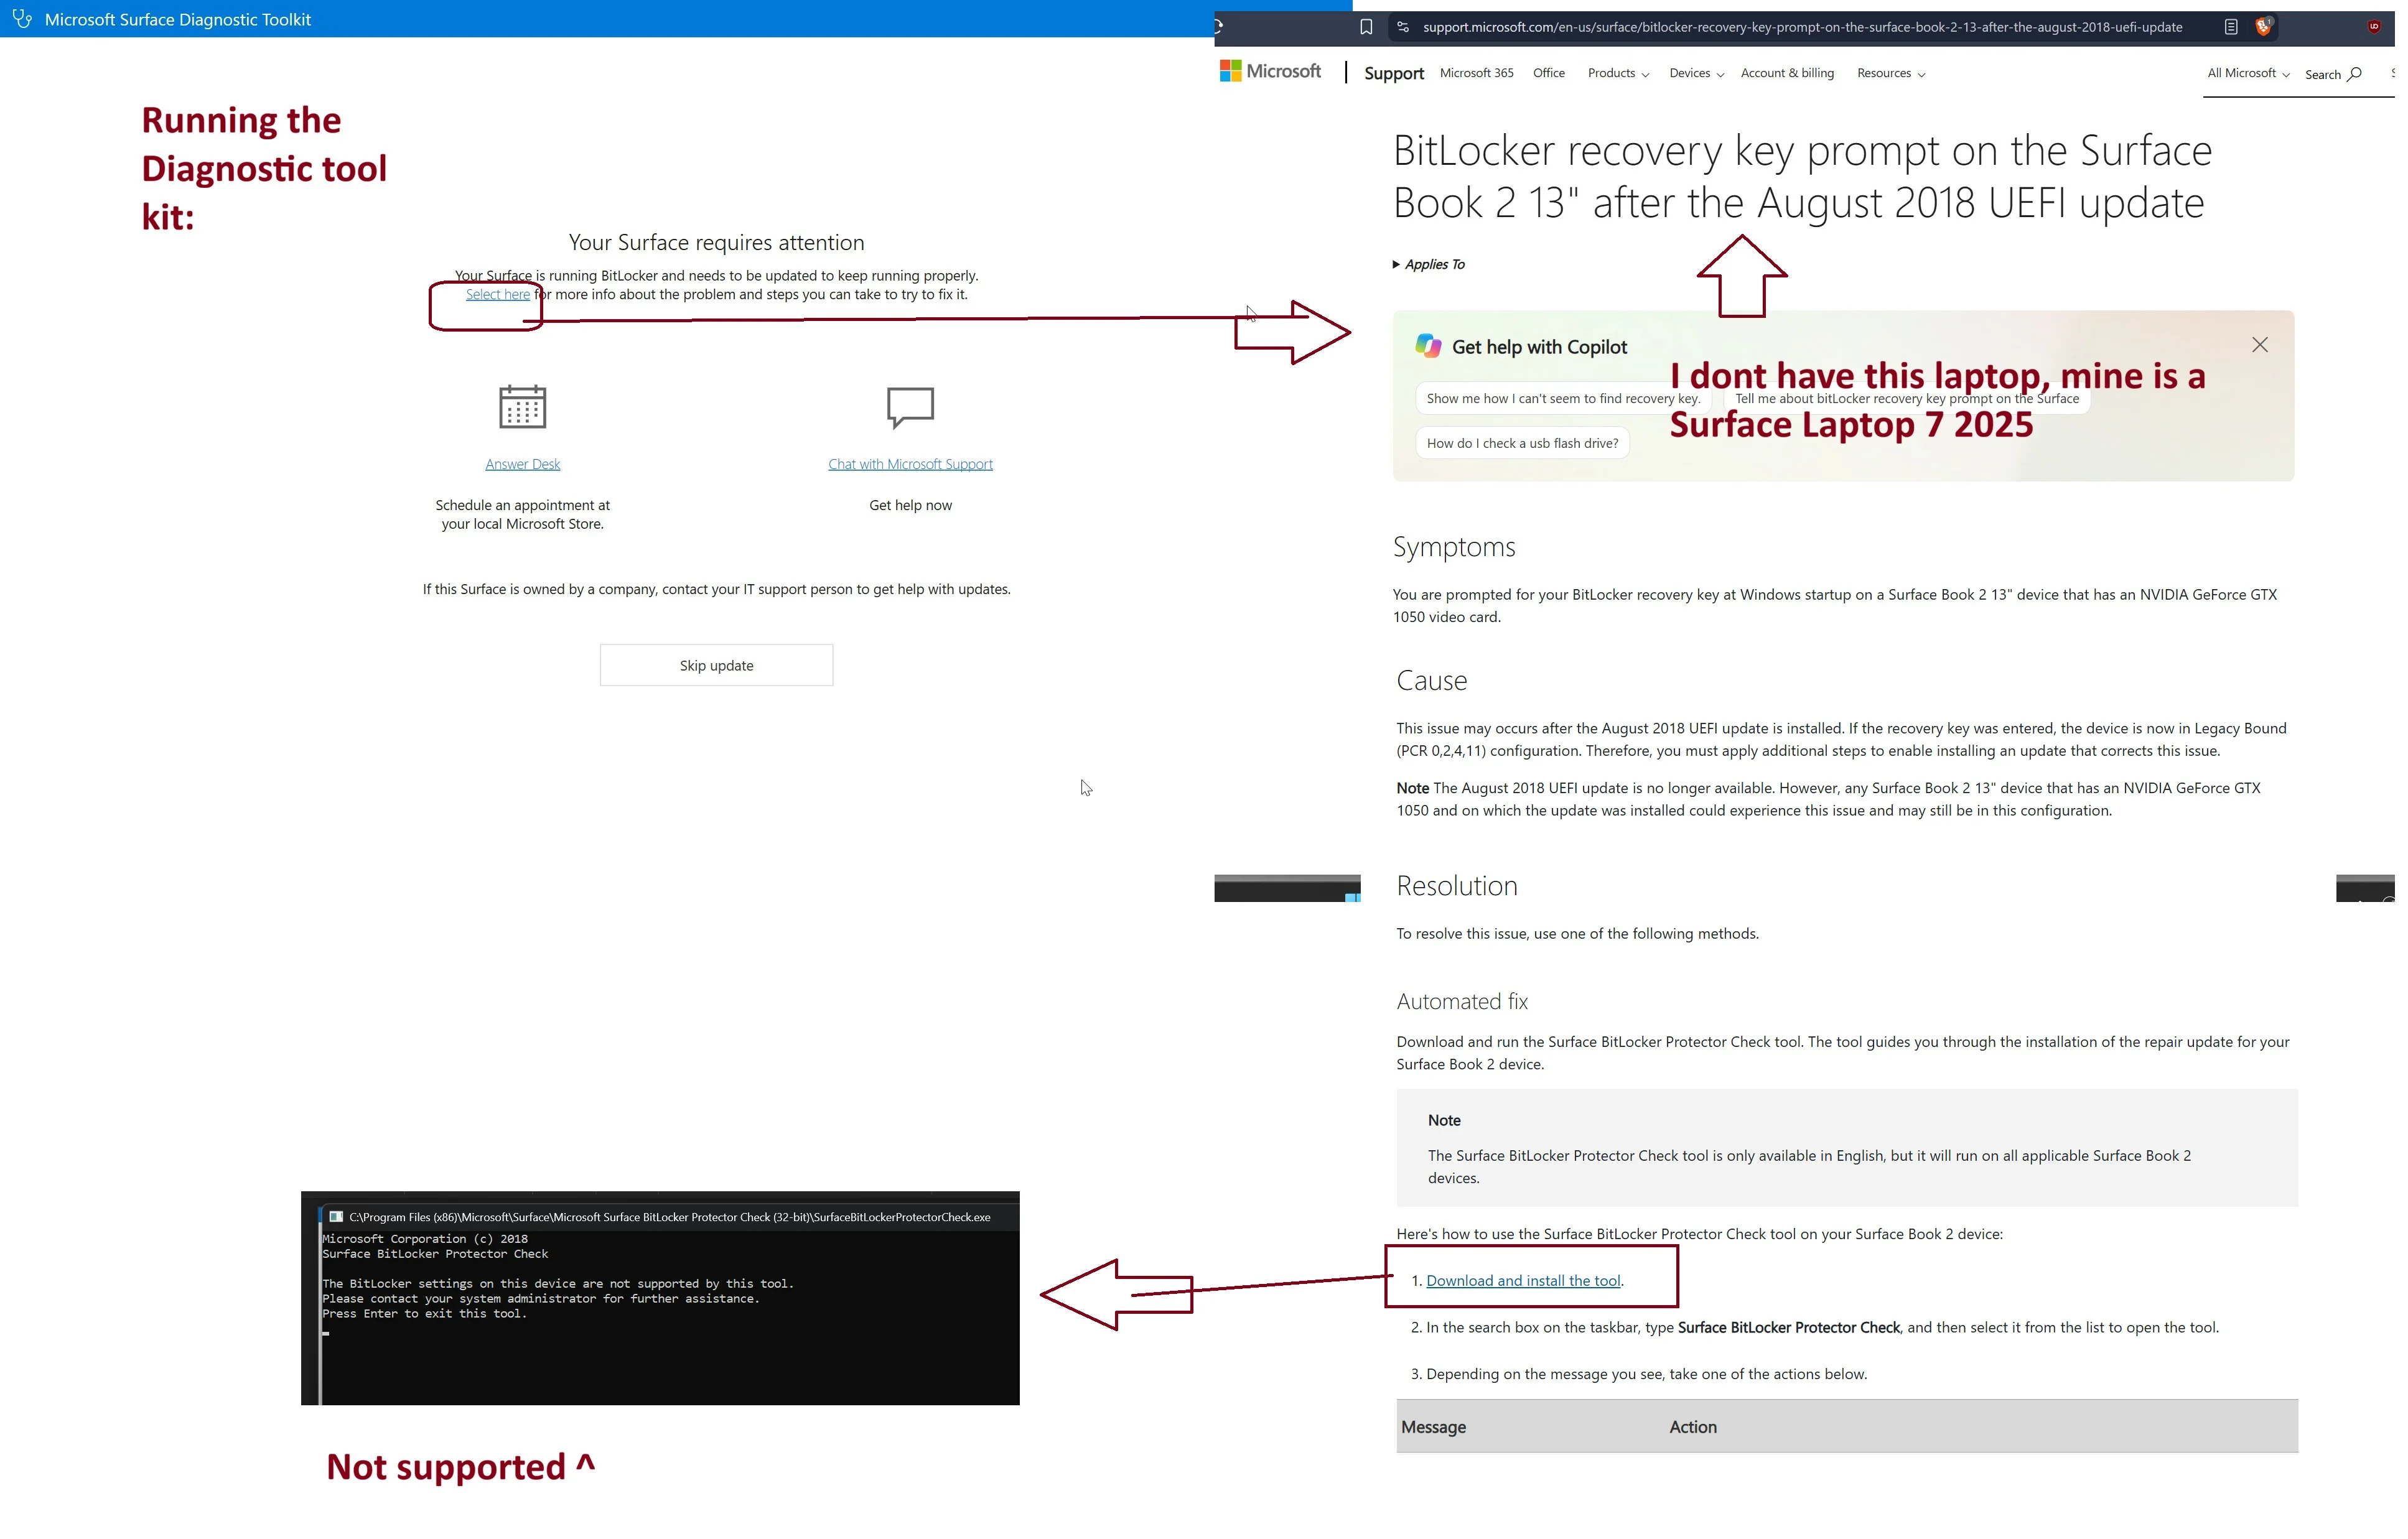
Diagnostic bitlocker tool.webp


Final Result of Diagnostic:

Diagnostic results.webp


I Went back to event viewer, I see Bitlocker Issue lining up with the time of the shutdown crashes, but that could be an AFTER effect from the unexpected shutdown, not the cause? But I dont know:. I have NO issue logging in and do not have to enter a 48 character recovery key. Just enter the Pre-boot pin as normal from any shutdown/boot up.
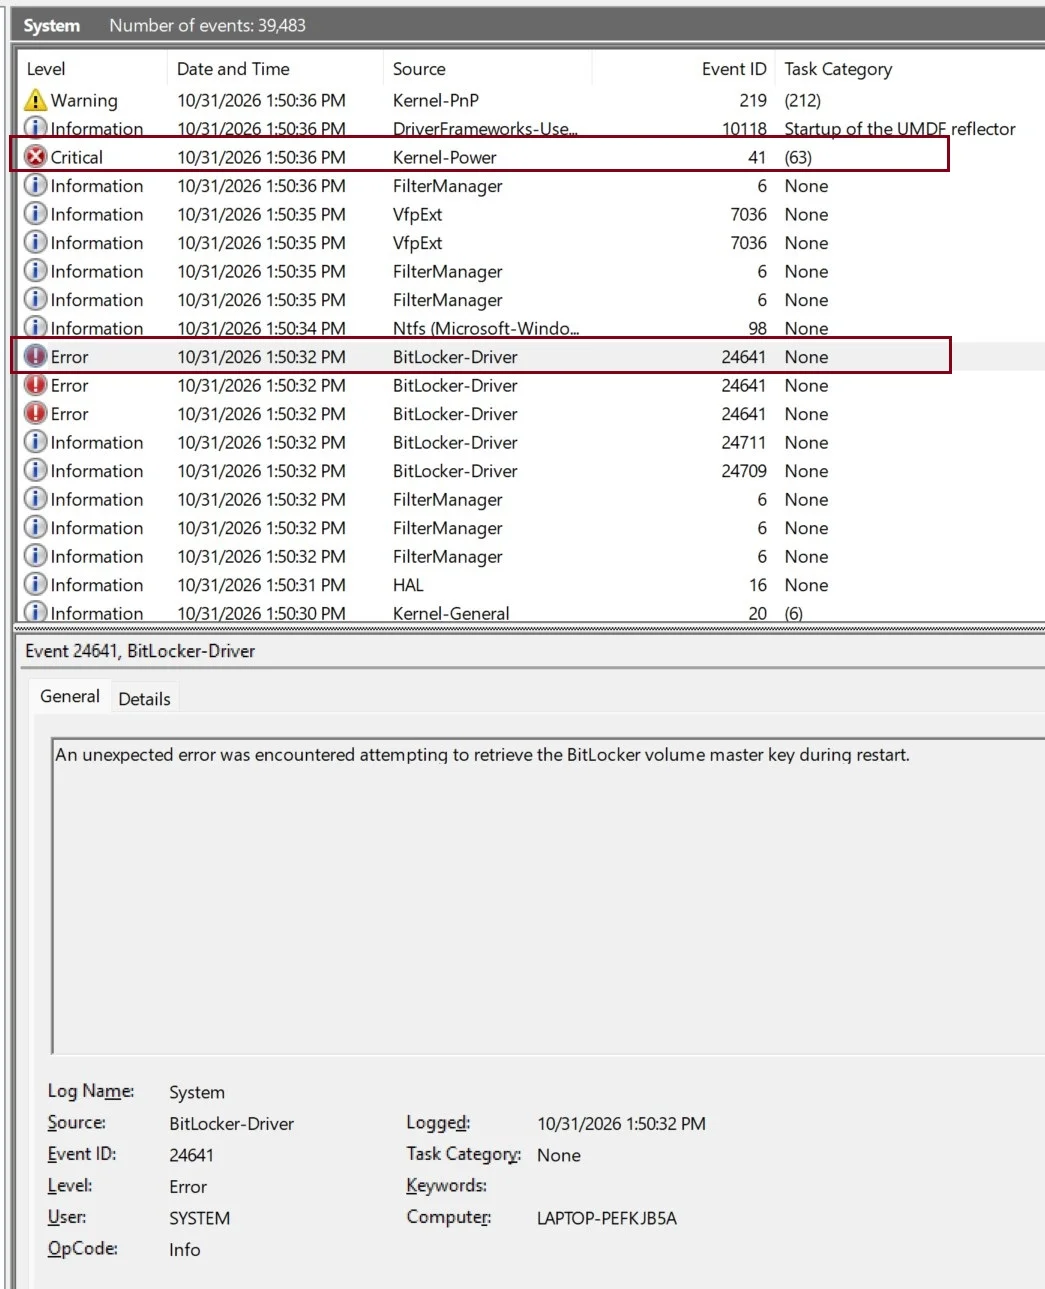
crash bitlocker error.webp


Claude's Analysis of the Event Viewer Export (But I dont trust it much):
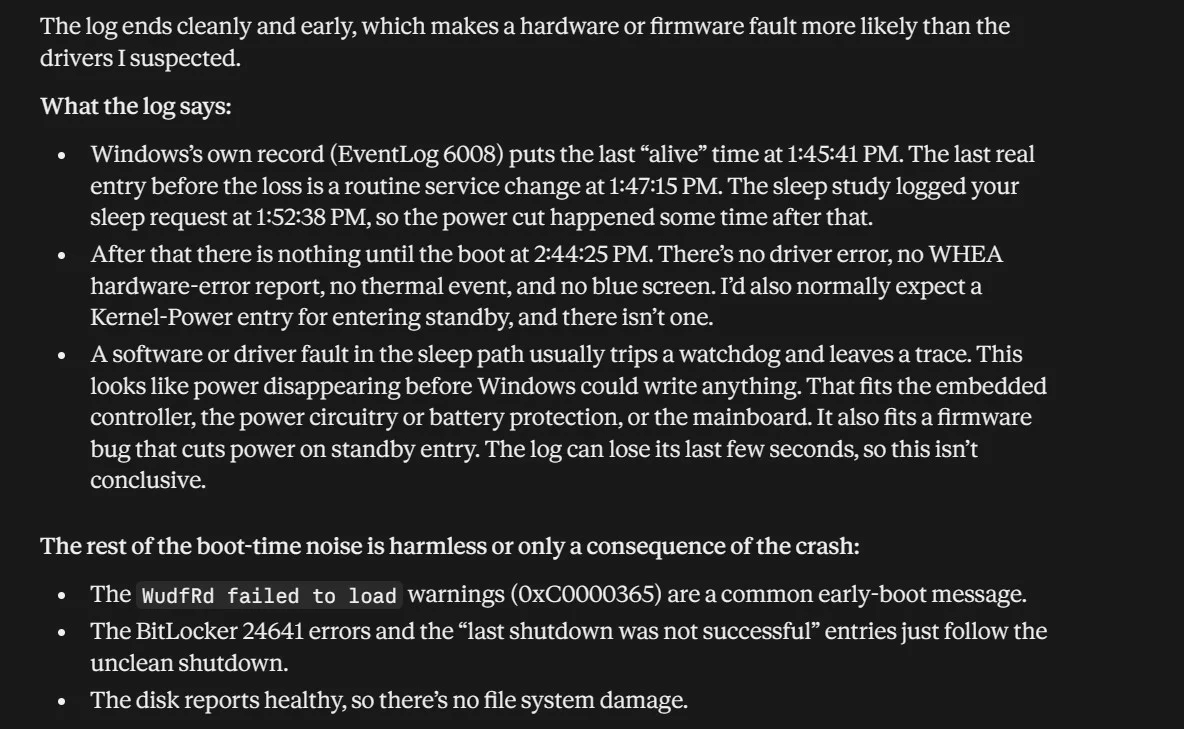
Claude Analysis of Event viewer.webp


Open to ideas?
And if it was Bitlocker causing this, should I Turn Off or just suspend bitlicker? With Turn-Off, I'd hate to have to re-setup the backup key and pin again if its not the cause, but simply an after effect of the crash.
 
Windows Build/Version
Windows 11 Pro, 25H2 OS build 26200.9711.
Last edited:

My Computer My Computer

At a glance

windwos 11 pro
OS
windwos 11 pro
Use the following instructions to gather the necessary log files. Put them all in a folder, zip the folder, then upload the Zipped folder to Google Drive or any cloud provider. Post a share link to the folder here..
@zbook will take a look when he comes online and will give you farther instructions..
 

My Computers My Computers

  • At a glance

    Windows 11 Pro 26H2 26300.9457i9-10900 10 core 20 threads32 gbnone-Intel UHD Graphics 630
    OS
    Windows 11 Pro 26H2 26300.9457
    Computer type
    PC/Desktop
    Manufacturer/Model
    Dell Optiplex 7080
    CPU
    i9-10900 10 core 20 threads
    Motherboard
    DELL 0J37VM
    Memory
    32 gb
    Graphics Card(s)
    none-Intel UHD Graphics 630
    Sound Card
    Integrated Realtek
    Monitor(s) Displays
    Benq 27
    Screen Resolution
    2560x1440
    Hard Drives
    2x1tb Solidigm m.2 nvme /External drives 512gb Samsung m.2 sata+2tb Kingston m2.nvme
    PSU
    500w
    Case
    MT
    Cooling
    Dell Premium
    Keyboard
    Logitech wired
    Mouse
    Logitech wireless
    Internet Speed
    so slow I'm too embarrassed to tell
    Browser
    #1 Edge #2 Firefox
    Antivirus
    Defender+MWB Premium
  • At a glance

    Windows 11 Pro 24H2 26200.9457AMD Ryzen 7 6800U32 gbintegrated
    Operating System
    Windows 11 Pro 24H2 26200.9457
    Computer type
    PC/Desktop
    Manufacturer/Model
    Beelink Mini PC SER5
    CPU
    AMD Ryzen 7 6800U
    Memory
    32 gb
    Graphics card(s)
    integrated
    Sound Card
    integrated
    Monitor(s) Displays
    Benq 27
    Screen Resolution
    2560x1440
    Hard Drives
    1TB Crucial nvme
    Keyboard
    Logitech wired
    Mouse
    Logitech wireless
    Internet Speed
    still too embarrassed to tell
    Browser
    Firefox
    Antivirus
    Defender
  • System 3 is non compliant Dell 9020 i7-4770/24gb ram Win11 PRO 26200.9457
Use the following instructions to gather the necessary log files. Put them all in a folder, zip the folder, then upload the Zipped folder to Google Drive or any cloud provider. Post a share link to the folder here..
@zbook will take a look when he comes online and will give you farther instructions..
Thanks, Done, Uploaded to the Google Folder: V2 log collector LAPTOP-(2026-10-31_16-22-18).zip
 

My Computer My Computer

At a glance

windwos 11 pro
OS
windwos 11 pro
Please open a thread in the Microsoft Surface forum and post a link into this forum.


Surface Laptop for Business 7th Edition with Intel
 

My Computer My Computer

At a glance

Windows 10Intel(R) Core(TM) i7-4800MQ CPU @ 2.70GHz16 GB Total: Manufacturer : Samsung MemoryTyp...NVIDIA Quadro K3100M; Intel(R) HD Graphics 4600
OS
Windows 10
Computer type
Laptop
Manufacturer/Model
HP
CPU
Intel(R) Core(TM) i7-4800MQ CPU @ 2.70GHz
Motherboard
Product : 190A Version : KBC Version 94.56
Memory
16 GB Total: Manufacturer : Samsung MemoryType : DDR3 FormFactor : SODIMM Capacity : 8GB Speed : 1600
Graphics Card(s)
NVIDIA Quadro K3100M; Intel(R) HD Graphics 4600
Sound Card
IDT High Definition Audio CODEC; PNP Device ID HDAUDIO\FUNC_01&VEN_111D&DEV_76E0
Hard Drives
Model Hitachi HTS727575A9E364
Antivirus
Microsoft Defender
Other Info
Mobile Workstation
Have you tried to disable Fast Startup? That is a frequent cause of such issues.

IMPORTANT: I am talking about fast startup in Windows, not in BIOS settings.


Screenshot 2026-10-31 211900.webp
 

My Computers My Computers

  • At a glance

    Win11 Pro 26H2Intel i7-14650HX32 GBBuilt-in Intel Graphics
    OS
    Win11 Pro 26H2
    Computer type
    PC/Desktop
    Manufacturer/Model
    Acemagic Matrix M5
    CPU
    Intel i7-14650HX
    Memory
    32 GB
    Graphics Card(s)
    Built-in Intel Graphics
    Sound Card
    Integrated
    Monitor(s) Displays
    Varies as machine will often be moved to locations with different monitors
    Screen Resolution
    Varies
    Hard Drives
    1 x 1TB Gen 4 NVMe SSD
    PSU
    120W Power Brick (an especially compact GaN charger)
    Keyboard
    Corsair K70 Max RGB Magnetic Keyboard
    Mouse
    Logitech MX Master 3
    Internet Speed
    1Gb Up / 1 Gb Down
    Browser
    Edge
    Antivirus
    Windows Defender
  • At a glance

    Win11 Pro 26H2Intel i7-1255U16 GBIntel Iris Xe Graphics
    Operating System
    Win11 Pro 26H2
    Computer type
    Laptop
    Manufacturer/Model
    Lenovo ThinkBook 13x Gen 2
    CPU
    Intel i7-1255U
    Memory
    16 GB
    Graphics card(s)
    Intel Iris Xe Graphics
    Sound Card
    Realtek® ALC3306-CG codec
    Monitor(s) Displays
    13.3-inch IPS Display
    Screen Resolution
    WQXGA (2560 x 1600)
    Hard Drives
    4 TB 4 x 4 NVMe SSD
    PSU
    USB-C / Thunderbolt 4 Power / Charging Using an Anker 160W Charger
    Keyboard
    Backlit, spill resistant keyboard
    Mouse
    Buttonless Glass Precision Touchpad
    Internet Speed
    1Gb Up / 1Gb Down
    Browser
    Edge
    Antivirus
    Windows Defender
    Other Info
    WiFi 6e / Bluetooth 5.1 / Facial Recognition / Fingerprint Sensor / ToF (Time of Flight) Human Presence Sensor
Have you tried to disable Fast Startup? That is a frequent cause of such issues.

IMPORTANT: I am talking about fast startup in Windows, not in BIOS settings.


View attachment 188495
I just checked, my fast start up in windows is already disabled.
cvA7ylhjCo.webp
 
Last edited:

My Computer My Computer

At a glance

windwos 11 pro
OS
windwos 11 pro
Please open a thread in the Microsoft Surface forum and post a link into this forum.


Surface Laptop for Business 7th Edition with Intel
Okay, I'll give it a try tomorrow.


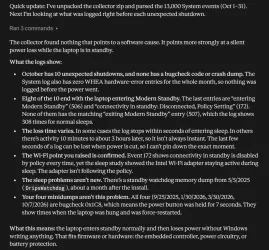
Also I uploaded V2 Log to Claude to review everything, it's response is attached. So yeah I guess IF Claude is correct, its not a Windows thing, its Surface Firmware or hardware.
Also was thinking if it was a recent firmware/windows update, I could see what happens after the next patch Tuesday or even update to 26H2, incase it effects it somehow.
 

Attachments

  • v2 Log from Claude.webp
    v2 Log from Claude.webp
    172 KB · Views: 1
Last edited:

My Computer My Computer

At a glance

windwos 11 pro
OS
windwos 11 pro
What is attached to the surface laptop?

Disconnect anything that is plug and play.


The BSOD bugcheck was: 0x000001c8

There were many beginning September 2026.


Code:
Bug Check 0x1C8: MANUALLY_INITIATED_POWER_BUTTON_HOLD

Summarize this article for me
The MANUALLY_INITIATED_POWER_BUTTON_HOLD has a value of 0x000001C8.

The system was configured to initiate a bugcheck when the user holds the power button for a specified length of time. This is a diagnostic bugcheck used to capture a dump when the system is about to be hard reset with a long power button hold.

 Important

This article is for programmers. If you're a customer who has received a blue screen error code while using your computer, see Troubleshoot blue screen errors.

Note that when this bug check occurs instead of the standard "blue screen" being displayed, a black background with the following text is displayed along with a % completion indicator:

“Please release the power button. We just need a few more seconds to shut down.”

MANUALLY_INITIATED_POWER_BUTTON_HOLD Parameters
The following parameters are displayed on the blue screen.

Parameter    Description
1    Time in milliseconds the power button was held down.
2    Pointer to nt!_POP_POWER_BUTTON_TRIAGE_BLOCK.
3    Reserved.
4    Reserved.


These were some event viewer entries:


Code:
Event[1763]
  Log Name: System
  Source: Microsoft-Windows-WER-SystemErrorReporting
  Date: 2026-10-07T13:52:16.7280000Z
  Event ID: 1001
  Task: N/A
  Level: Error
  Opcode: Info
  Keyword: N/A
  User: S-1-5-18
  User Name: NT AUTHORITY\SYSTEM
  Computer: LAPTOP-PEFKJB5A
  Description:
The computer has rebooted from a bugcheck.  The bugcheck was: 0x000001c8 (0x000000000704b009, 0xfffff80297b07c40, 0x0000000000001b58, 0x0000000000000000). A dump was saved in: C:\Windows\Minidump\100726-16718-01.dmp. Report Id: d4977284-6e53-4709-a801-c2d2f85dc79d.


Code:
Event[13106]
  Log Name: System
  Source: Microsoft-Windows-WindowsUpdateClient
  Date: 2026-10-31T16:13:06.6710000Z
  Event ID: 43
  Task: Windows Update Agent
  Level: Information
  Opcode: Installation
  Keyword: Installation,Started,
  User: S-1-5-18
  User Name: NT AUTHORITY\SYSTEM
  Computer: LAPTOP-PEFKJB5A
  Description:
Installation Started: Windows has started installing the following update: 9WZDNCRFJB8P-MICROSOFT.SURFACEHUB

Event[13107]
  Log Name: System
  Source: Microsoft-Windows-WindowsUpdateClient
  Date: 2026-10-31T16:13:07.0970000Z
  Event ID: 20
  Task: Windows Update Agent
  Level: Error
  Opcode: Installation
  Keyword: Installation,Failure,
  User: S-1-5-18
  User Name: NT AUTHORITY\SYSTEM
  Computer: LAPTOP-PEFKJB5A
  Description:
Installation Failure: Windows failed to install the following update with error 0x80073D02: 9WZDNCRFJB8P-MICROSOFT.SURFACEHUB.


Code:
Event[13100]
  Log Name: System
  Source: Microsoft-Windows-WindowsUpdateClient
  Date: 2026-10-31T16:12:38.9300000Z
  Event ID: 43
  Task: Windows Update Agent
  Level: Information
  Opcode: Installation
  Keyword: Installation,Started,
  User: S-1-5-18
  User Name: NT AUTHORITY\SYSTEM
  Computer: LAPTOP-PEFKJB5A
  Description:
Installation Started: Windows has started installing the following update: 9NTXGKQ8P7N0-MicrosoftWindows.CrossDevice

Event[13101]
  Log Name: System
  Source: Microsoft-Windows-WindowsUpdateClient
  Date: 2026-10-31T16:12:39.5610000Z
  Event ID: 20
  Task: Windows Update Agent
  Level: Error
  Opcode: Installation
  Keyword: Installation,Failure,
  User: S-1-5-18
  User Name: NT AUTHORITY\SYSTEM
  Computer: LAPTOP-PEFKJB5A
  Description:
Installation Failure: Windows failed to install the following update with error 0x80073D02: 9NTXGKQ8P7N0-MicrosoftWindows.CrossDevice.


Code:
Event[12997]
  Log Name: System
  Source: Microsoft-Windows-BitLocker-Driver
  Date: 2026-10-31T15:07:54.7030000Z
  Event ID: 24641
  Task: N/A
  Level: Error
  Opcode: Info
  Keyword: N/A
  User: N/A
  User Name: N/A
  Computer: LAPTOP-PEFKJB5A
  Description:
An unexpected error was encountered attempting to retrieve the BitLocker volume master key during restart.

Event[12998]
  Log Name: System
  Source: Microsoft-Windows-BitLocker-Driver
  Date: 2026-10-31T15:07:54.7030000Z
  Event ID: 24641
  Task: N/A
  Level: Error
  Opcode: Info
  Keyword: N/A
  User: N/A
  User Name: N/A
  Computer: LAPTOP-PEFKJB5A
  Description:
An unexpected error was encountered attempting to retrieve the BitLocker volume master key during restart.
 

My Computer My Computer

At a glance

Windows 10Intel(R) Core(TM) i7-4800MQ CPU @ 2.70GHz16 GB Total: Manufacturer : Samsung MemoryTyp...NVIDIA Quadro K3100M; Intel(R) HD Graphics 4600
OS
Windows 10
Computer type
Laptop
Manufacturer/Model
HP
CPU
Intel(R) Core(TM) i7-4800MQ CPU @ 2.70GHz
Motherboard
Product : 190A Version : KBC Version 94.56
Memory
16 GB Total: Manufacturer : Samsung MemoryType : DDR3 FormFactor : SODIMM Capacity : 8GB Speed : 1600
Graphics Card(s)
NVIDIA Quadro K3100M; Intel(R) HD Graphics 4600
Sound Card
IDT High Definition Audio CODEC; PNP Device ID HDAUDIO\FUNC_01&VEN_111D&DEV_76E0
Hard Drives
Model Hitachi HTS727575A9E364
Antivirus
Microsoft Defender
Other Info
Mobile Workstation
What is attached to the surface laptop?

Disconnect anything that is plug and play.


The BSOD bugcheck was: 0x000001c8

There were many beginning September 2026.

I have not had anything attached to my laptop, USB, mouse, etc....

Regards to 0x1C8 on 10/7 That would just be me holding the power button manually right? I must have been impatient with something that happened. But I assume that is separate from the modern standby going into a shutdown.

Seems to have started 10/27, or really ramped up. But that also because i've been testing it more now, putting it into modern standby after trying things.

Thirteen are silent power losses (code 0), and one is the 10/7 hang/manual shut down.
  • From 9/2 to 10/26 there were 8 events in 55 days, about one a week.
  • Since 10/27 there have been 6 in about 4 days, over one a day. A tenfold jump after the 10/26 firmware and 10/27 update.
 

My Computer My Computer

At a glance

windwos 11 pro
OS
windwos 11 pro
The logs reported the BSODs starting 09/02/2026


Code:
9/4/2026 12:29 AM    Windows Error Reporting    Fault bucket , type 0
Event Name: BlueScreen
Response: Not available
Cab Id: 0

Problem signature:
P1: 1c8
P2: 3077009
P3: fffff80379b07520
P4: 1b58
P5: 0
P6: 10_0_26100
P7: 0_0
P8: 256_1
P9: 
P10: 

Attached files:
\\?\C:\Windows\Minidump\013026-14156-01.dmp
\\?\C:\Windows\SystemTemp\WER-14156-0.sysdata.xml
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.8ce075d9-a734-4ccd-bf6e-8e55dc0a5b21.tmp.WERInternalMetadata.xml
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.81627374-00cb-46dd-b51f-27249bb9e6a6.tmp.csv
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.ece2cf57-0798-447d-a214-f4ba769bd4e4.tmp.txt
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.0ea427bc-9398-4b38-b5af-b2dcb1974a57.tmp.xml

These files may be available here:
\\?\C:\ProgramData\Microsoft\Windows\WER\ReportQueue\Kernel_1c8_cbbc9e3f1a13a31b31426db79bc615a2eec94_00000000_6492e93a-9681-4901-9754-e2f154aebd26

Analysis symbol: 
Rechecking for solution: 0
Report Id: 8f9c3576-29cd-40a3-b91f-d659ff148cb5
Report Status: 2051
Hashed bucket: 
Cab Guid: 0
9/3/2026 11:26 PM    Windows Error Reporting    Fault bucket , type 0
Event Name: BlueScreen
Response: Not available
Cab Id: 0

Problem signature:
P1: 1c8
P2: 3077009
P3: fffff80379b07520
P4: 1b58
P5: 0
P6: 10_0_26100
P7: 0_0
P8: 256_1
P9: 
P10: 

Attached files:
\\?\C:\Windows\Minidump\013026-14156-01.dmp
\\?\C:\Windows\SystemTemp\WER-14156-0.sysdata.xml
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.8ce075d9-a734-4ccd-bf6e-8e55dc0a5b21.tmp.WERInternalMetadata.xml
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.81627374-00cb-46dd-b51f-27249bb9e6a6.tmp.csv
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.ece2cf57-0798-447d-a214-f4ba769bd4e4.tmp.txt
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.0ea427bc-9398-4b38-b5af-b2dcb1974a57.tmp.xml

These files may be available here:
\\?\C:\ProgramData\Microsoft\Windows\WER\ReportQueue\Kernel_1c8_cbbc9e3f1a13a31b31426db79bc615a2eec94_00000000_6492e93a-9681-4901-9754-e2f154aebd26

Analysis symbol: 
Rechecking for solution: 0
Report Id: 8f9c3576-29cd-40a3-b91f-d659ff148cb5
Report Status: 2051
Hashed bucket: 
Cab Guid: 0
9/3/2026 10:57 PM    Windows Error Reporting    Fault bucket , type 0
Event Name: BlueScreen
Response: Not available
Cab Id: 0

Problem signature:
P1: 1c8
P2: 3077009
P3: fffff80379b07520
P4: 1b58
P5: 0
P6: 10_0_26100
P7: 0_0
P8: 256_1
P9: 
P10: 

Attached files:
\\?\C:\Windows\Minidump\013026-14156-01.dmp
\\?\C:\Windows\SystemTemp\WER-14156-0.sysdata.xml
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.8ce075d9-a734-4ccd-bf6e-8e55dc0a5b21.tmp.WERInternalMetadata.xml
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.81627374-00cb-46dd-b51f-27249bb9e6a6.tmp.csv
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.ece2cf57-0798-447d-a214-f4ba769bd4e4.tmp.txt
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.0ea427bc-9398-4b38-b5af-b2dcb1974a57.tmp.xml

These files may be available here:
\\?\C:\ProgramData\Microsoft\Windows\WER\ReportQueue\Kernel_1c8_cbbc9e3f1a13a31b31426db79bc615a2eec94_00000000_6492e93a-9681-4901-9754-e2f154aebd26

Analysis symbol: 
Rechecking for solution: 0
Report Id: 8f9c3576-29cd-40a3-b91f-d659ff148cb5
Report Status: 2051
Hashed bucket: 
Cab Guid: 0
9/3/2026 8:51 PM    Windows Error Reporting    Fault bucket , type 0
Event Name: BlueScreen
Response: Not available
Cab Id: 0

Problem signature:
P1: 1c8
P2: 3077009
P3: fffff80379b07520
P4: 1b58
P5: 0
P6: 10_0_26100
P7: 0_0
P8: 256_1
P9: 
P10: 

Attached files:
\\?\C:\Windows\Minidump\013026-14156-01.dmp
\\?\C:\Windows\SystemTemp\WER-14156-0.sysdata.xml
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.8ce075d9-a734-4ccd-bf6e-8e55dc0a5b21.tmp.WERInternalMetadata.xml
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.81627374-00cb-46dd-b51f-27249bb9e6a6.tmp.csv
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.ece2cf57-0798-447d-a214-f4ba769bd4e4.tmp.txt
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.0ea427bc-9398-4b38-b5af-b2dcb1974a57.tmp.xml

These files may be available here:
\\?\C:\ProgramData\Microsoft\Windows\WER\ReportQueue\Kernel_1c8_cbbc9e3f1a13a31b31426db79bc615a2eec94_00000000_6492e93a-9681-4901-9754-e2f154aebd26

Analysis symbol: 
Rechecking for solution: 0
Report Id: 8f9c3576-29cd-40a3-b91f-d659ff148cb5
Report Status: 2051
Hashed bucket: 
Cab Guid: 0
9/3/2026 8:50 PM    Windows Error Reporting    Fault bucket , type 0
Event Name: BlueScreen
Response: Not available
Cab Id: 0

Problem signature:
P1: 1c8
P2: 3077009
P3: fffff80379b07520
P4: 1b58
P5: 0
P6: 10_0_26100
P7: 0_0
P8: 256_1
P9: 
P10: 

Attached files:
\\?\C:\Windows\Minidump\013026-14156-01.dmp
\\?\C:\Windows\SystemTemp\WER-14156-0.sysdata.xml
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.8ce075d9-a734-4ccd-bf6e-8e55dc0a5b21.tmp.WERInternalMetadata.xml
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.81627374-00cb-46dd-b51f-27249bb9e6a6.tmp.csv
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.ece2cf57-0798-447d-a214-f4ba769bd4e4.tmp.txt
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.0ea427bc-9398-4b38-b5af-b2dcb1974a57.tmp.xml

These files may be available here:
\\?\C:\ProgramData\Microsoft\Windows\WER\ReportQueue\Kernel_1c8_cbbc9e3f1a13a31b31426db79bc615a2eec94_00000000_6492e93a-9681-4901-9754-e2f154aebd26

Analysis symbol: 
Rechecking for solution: 0
Report Id: 8f9c3576-29cd-40a3-b91f-d659ff148cb5
Report Status: 2051
Hashed bucket: 
Cab Guid: 0
9/3/2026 4:39 AM    Windows Error Reporting    Fault bucket , type 0
Event Name: BlueScreen
Response: Not available
Cab Id: 0

Problem signature:
P1: 1c8
P2: 3077009
P3: fffff80379b07520
P4: 1b58
P5: 0
P6: 10_0_26100
P7: 0_0
P8: 256_1
P9: 
P10: 

Attached files:
\\?\C:\Windows\Minidump\013026-14156-01.dmp
\\?\C:\Windows\SystemTemp\WER-14156-0.sysdata.xml
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.8ce075d9-a734-4ccd-bf6e-8e55dc0a5b21.tmp.WERInternalMetadata.xml
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.81627374-00cb-46dd-b51f-27249bb9e6a6.tmp.csv
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.ece2cf57-0798-447d-a214-f4ba769bd4e4.tmp.txt
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.0ea427bc-9398-4b38-b5af-b2dcb1974a57.tmp.xml

These files may be available here:
\\?\C:\ProgramData\Microsoft\Windows\WER\ReportQueue\Kernel_1c8_cbbc9e3f1a13a31b31426db79bc615a2eec94_00000000_6492e93a-9681-4901-9754-e2f154aebd26

Analysis symbol: 
Rechecking for solution: 0
Report Id: 8f9c3576-29cd-40a3-b91f-d659ff148cb5
Report Status: 2051
Hashed bucket: 
Cab Guid: 0
9/3/2026 3:29 AM    Windows Error Reporting    Fault bucket , type 0
Event Name: BlueScreen
Response: Not available
Cab Id: 0

Problem signature:
P1: 1c8
P2: 3077009
P3: fffff80379b07520
P4: 1b58
P5: 0
P6: 10_0_26100
P7: 0_0
P8: 256_1
P9: 
P10: 

Attached files:
\\?\C:\Windows\Minidump\013026-14156-01.dmp
\\?\C:\Windows\SystemTemp\WER-14156-0.sysdata.xml
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.8ce075d9-a734-4ccd-bf6e-8e55dc0a5b21.tmp.WERInternalMetadata.xml
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.81627374-00cb-46dd-b51f-27249bb9e6a6.tmp.csv
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.ece2cf57-0798-447d-a214-f4ba769bd4e4.tmp.txt
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.0ea427bc-9398-4b38-b5af-b2dcb1974a57.tmp.xml

These files may be available here:
\\?\C:\ProgramData\Microsoft\Windows\WER\ReportQueue\Kernel_1c8_cbbc9e3f1a13a31b31426db79bc615a2eec94_00000000_6492e93a-9681-4901-9754-e2f154aebd26

Analysis symbol: 
Rechecking for solution: 0
Report Id: 8f9c3576-29cd-40a3-b91f-d659ff148cb5
Report Status: 2051
Hashed bucket: 
Cab Guid: 0
9/3/2026 2:28 AM    Windows Error Reporting    Fault bucket , type 0
Event Name: BlueScreen
Response: Not available
Cab Id: 0

Problem signature:
P1: 1c8
P2: 3077009
P3: fffff80379b07520
P4: 1b58
P5: 0
P6: 10_0_26100
P7: 0_0
P8: 256_1
P9: 
P10: 

Attached files:
\\?\C:\Windows\Minidump\013026-14156-01.dmp
\\?\C:\Windows\SystemTemp\WER-14156-0.sysdata.xml
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.8ce075d9-a734-4ccd-bf6e-8e55dc0a5b21.tmp.WERInternalMetadata.xml
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.81627374-00cb-46dd-b51f-27249bb9e6a6.tmp.csv
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.ece2cf57-0798-447d-a214-f4ba769bd4e4.tmp.txt
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.0ea427bc-9398-4b38-b5af-b2dcb1974a57.tmp.xml

These files may be available here:
\\?\C:\ProgramData\Microsoft\Windows\WER\ReportQueue\Kernel_1c8_cbbc9e3f1a13a31b31426db79bc615a2eec94_00000000_6492e93a-9681-4901-9754-e2f154aebd26

Analysis symbol: 
Rechecking for solution: 0
Report Id: 8f9c3576-29cd-40a3-b91f-d659ff148cb5
Report Status: 2051
Hashed bucket: 
Cab Guid: 0
9/3/2026 12:53 AM    Windows Error Reporting    Fault bucket , type 0
Event Name: BlueScreen
Response: Not available
Cab Id: 0

Problem signature:
P1: 1c8
P2: 3077009
P3: fffff80379b07520
P4: 1b58
P5: 0
P6: 10_0_26100
P7: 0_0
P8: 256_1
P9: 
P10: 

Attached files:
\\?\C:\Windows\Minidump\013026-14156-01.dmp
\\?\C:\Windows\SystemTemp\WER-14156-0.sysdata.xml
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.8ce075d9-a734-4ccd-bf6e-8e55dc0a5b21.tmp.WERInternalMetadata.xml
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.81627374-00cb-46dd-b51f-27249bb9e6a6.tmp.csv
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.ece2cf57-0798-447d-a214-f4ba769bd4e4.tmp.txt
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.0ea427bc-9398-4b38-b5af-b2dcb1974a57.tmp.xml

These files may be available here:
\\?\C:\ProgramData\Microsoft\Windows\WER\ReportQueue\Kernel_1c8_cbbc9e3f1a13a31b31426db79bc615a2eec94_00000000_6492e93a-9681-4901-9754-e2f154aebd26

Analysis symbol: 
Rechecking for solution: 0
Report Id: 8f9c3576-29cd-40a3-b91f-d659ff148cb5
Report Status: 2051
Hashed bucket: 
Cab Guid: 0
9/3/2026 12:04 AM    Windows Error Reporting    Fault bucket , type 0
Event Name: BlueScreen
Response: Not available
Cab Id: 0

Problem signature:
P1: 1c8
P2: 3077009
P3: fffff80379b07520
P4: 1b58
P5: 0
P6: 10_0_26100
P7: 0_0
P8: 256_1
P9: 
P10: 

Attached files:
\\?\C:\Windows\Minidump\013026-14156-01.dmp
\\?\C:\Windows\SystemTemp\WER-14156-0.sysdata.xml
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.8ce075d9-a734-4ccd-bf6e-8e55dc0a5b21.tmp.WERInternalMetadata.xml
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.81627374-00cb-46dd-b51f-27249bb9e6a6.tmp.csv
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.ece2cf57-0798-447d-a214-f4ba769bd4e4.tmp.txt
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.0ea427bc-9398-4b38-b5af-b2dcb1974a57.tmp.xml

These files may be available here:
\\?\C:\ProgramData\Microsoft\Windows\WER\ReportQueue\Kernel_1c8_cbbc9e3f1a13a31b31426db79bc615a2eec94_00000000_6492e93a-9681-4901-9754-e2f154aebd26

Analysis symbol: 
Rechecking for solution: 0
Report Id: 8f9c3576-29cd-40a3-b91f-d659ff148cb5
Report Status: 2051
Hashed bucket: 
Cab Guid: 0
9/2/2026 11:10 PM    Windows Error Reporting    Fault bucket , type 0
Event Name: BlueScreen
Response: Not available
Cab Id: 0

Problem signature:
P1: 1c8
P2: 3077009
P3: fffff80379b07520
P4: 1b58
P5: 0
P6: 10_0_26100
P7: 0_0
P8: 256_1
P9: 
P10: 

Attached files:
\\?\C:\Windows\Minidump\013026-14156-01.dmp
\\?\C:\Windows\SystemTemp\WER-14156-0.sysdata.xml
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.8ce075d9-a734-4ccd-bf6e-8e55dc0a5b21.tmp.WERInternalMetadata.xml
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.81627374-00cb-46dd-b51f-27249bb9e6a6.tmp.csv
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.ece2cf57-0798-447d-a214-f4ba769bd4e4.tmp.txt
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.0ea427bc-9398-4b38-b5af-b2dcb1974a57.tmp.xml

These files may be available here:
\\?\C:\ProgramData\Microsoft\Windows\WER\ReportQueue\Kernel_1c8_cbbc9e3f1a13a31b31426db79bc615a2eec94_00000000_6492e93a-9681-4901-9754-e2f154aebd26

Analysis symbol: 
Rechecking for solution: 0
Report Id: 8f9c3576-29cd-40a3-b91f-d659ff148cb5
Report Status: 2051
Hashed bucket: 
Cab Guid: 0
9/2/2026 8:21 PM    Windows Error Reporting    Fault bucket , type 0
Event Name: BlueScreen
Response: Not available
Cab Id: 0

Problem signature:
P1: 1c8
P2: 3077009
P3: fffff80379b07520
P4: 1b58
P5: 0
P6: 10_0_26100
P7: 0_0
P8: 256_1
P9: 
P10: 

Attached files:
\\?\C:\Windows\Minidump\013026-14156-01.dmp
\\?\C:\Windows\SystemTemp\WER-14156-0.sysdata.xml
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.8ce075d9-a734-4ccd-bf6e-8e55dc0a5b21.tmp.WERInternalMetadata.xml
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.81627374-00cb-46dd-b51f-27249bb9e6a6.tmp.csv
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.ece2cf57-0798-447d-a214-f4ba769bd4e4.tmp.txt
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.0ea427bc-9398-4b38-b5af-b2dcb1974a57.tmp.xml

These files may be available here:
\\?\C:\ProgramData\Microsoft\Windows\WER\ReportQueue\Kernel_1c8_cbbc9e3f1a13a31b31426db79bc615a2eec94_00000000_6492e93a-9681-4901-9754-e2f154aebd26

Analysis symbol: 
Rechecking for solution: 0
Report Id: 8f9c3576-29cd-40a3-b91f-d659ff148cb5
Report Status: 2051
Hashed bucket: 
Cab Guid: 0
9/2/2026 7:20 PM    Windows Error Reporting    Fault bucket , type 0
Event Name: BlueScreen
Response: Not available
Cab Id: 0

Problem signature:
P1: 1c8
P2: 3077009
P3: fffff80379b07520
P4: 1b58
P5: 0
P6: 10_0_26100
P7: 0_0
P8: 256_1
P9: 
P10: 

Attached files:
\\?\C:\Windows\Minidump\013026-14156-01.dmp
\\?\C:\Windows\SystemTemp\WER-14156-0.sysdata.xml
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.8ce075d9-a734-4ccd-bf6e-8e55dc0a5b21.tmp.WERInternalMetadata.xml
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.81627374-00cb-46dd-b51f-27249bb9e6a6.tmp.csv
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.ece2cf57-0798-447d-a214-f4ba769bd4e4.tmp.txt
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.0ea427bc-9398-4b38-b5af-b2dcb1974a57.tmp.xml

These files may be available here:
\\?\C:\ProgramData\Microsoft\Windows\WER\ReportQueue\Kernel_1c8_cbbc9e3f1a13a31b31426db79bc615a2eec94_00000000_6492e93a-9681-4901-9754-e2f154aebd26

Analysis symbol: 
Rechecking for solution: 0
Report Id: 8f9c3576-29cd-40a3-b91f-d659ff148cb5
Report Status: 2051
Hashed bucket: 
Cab Guid: 0
9/2/2026 7:18 PM    Windows Error Reporting    Fault bucket , type 0
Event Name: BlueScreen
Response: Not available
Cab Id: 0

Problem signature:
P1: 1c8
P2: 3077009
P3: fffff80379b07520
P4: 1b58
P5: 0
P6: 10_0_26100
P7: 0_0
P8: 256_1
P9: 
P10: 

Attached files:
\\?\C:\Windows\Minidump\013026-14156-01.dmp
\\?\C:\Windows\SystemTemp\WER-14156-0.sysdata.xml
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.8ce075d9-a734-4ccd-bf6e-8e55dc0a5b21.tmp.WERInternalMetadata.xml
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.81627374-00cb-46dd-b51f-27249bb9e6a6.tmp.csv
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.ece2cf57-0798-447d-a214-f4ba769bd4e4.tmp.txt
\\?\C:\ProgramData\Microsoft\Windows\WER\Temp\WER.0ea427bc-9398-4b38-b5af-b2dcb1974a57.tmp.xml

These files may be available here:
\\?\C:\ProgramData\Microsoft\Windows\WER\ReportQueue\Kernel_1c8_cbbc9e3f1a13a31b31426db79bc615a2eec94_00000000_6492e93a-9681-4901-9754-e2f154aebd26

Analysis symbol: 
Rechecking for solution: 0
Report Id: 8f9c3576-29cd-40a3-b91f-d659ff148cb5
Report Status: 2051
Hashed bucket: 
Cab Guid: 0
 

My Computer My Computer

At a glance

Windows 10Intel(R) Core(TM) i7-4800MQ CPU @ 2.70GHz16 GB Total: Manufacturer : Samsung MemoryTyp...NVIDIA Quadro K3100M; Intel(R) HD Graphics 4600
OS
Windows 10
Computer type
Laptop
Manufacturer/Model
HP
CPU
Intel(R) Core(TM) i7-4800MQ CPU @ 2.70GHz
Motherboard
Product : 190A Version : KBC Version 94.56
Memory
16 GB Total: Manufacturer : Samsung MemoryType : DDR3 FormFactor : SODIMM Capacity : 8GB Speed : 1600
Graphics Card(s)
NVIDIA Quadro K3100M; Intel(R) HD Graphics 4600
Sound Card
IDT High Definition Audio CODEC; PNP Device ID HDAUDIO\FUNC_01&VEN_111D&DEV_76E0
Hard Drives
Model Hitachi HTS727575A9E364
Antivirus
Microsoft Defender
Other Info
Mobile Workstation
To clean up the spamming WER reports run admin command prompt:

net stop wersvc
del /q /f /s "%ProgramData%\Microsoft\Windows\WER\ReportQueue\*.*"
del /q /f /s "%ProgramData%\Microsoft\Windows\WER\Temp\*.*"
net start wersvc
 

My Computer My Computer

At a glance

Windows 10Intel(R) Core(TM) i7-4800MQ CPU @ 2.70GHz16 GB Total: Manufacturer : Samsung MemoryTyp...NVIDIA Quadro K3100M; Intel(R) HD Graphics 4600
OS
Windows 10
Computer type
Laptop
Manufacturer/Model
HP
CPU
Intel(R) Core(TM) i7-4800MQ CPU @ 2.70GHz
Motherboard
Product : 190A Version : KBC Version 94.56
Memory
16 GB Total: Manufacturer : Samsung MemoryType : DDR3 FormFactor : SODIMM Capacity : 8GB Speed : 1600
Graphics Card(s)
NVIDIA Quadro K3100M; Intel(R) HD Graphics 4600
Sound Card
IDT High Definition Audio CODEC; PNP Device ID HDAUDIO\FUNC_01&VEN_111D&DEV_76E0
Hard Drives
Model Hitachi HTS727575A9E364
Antivirus
Microsoft Defender
Other Info
Mobile Workstation
To make it less likely to miss BSODs run admin PS:

Code:
Get-CimInstance -ClassName Win32_OSRecoveryConfiguration | Select-Object AutoReboot
Get-CimInstance -ClassName Win32_OSRecoveryConfiguration | Set-CimInstance -Property @{AutoReboot=$false}
Get-CimInstance -ClassName Win32_OSRecoveryConfiguration | Select-Object AutoReboot

Get-CimInstance -ClassName Win32_OSRecoveryConfiguration | Select-Object DebugInfoType
Get-CimInstance -ClassName Win32_OSRecoveryConfiguration | Set-CimInstance -Property @{DebugInfoType=7}
Get-CimInstance -ClassName Win32_OSRecoveryConfiguration | Select-Object DebugInfoType

Get-CimInstance -ClassName Win32_PageFileUsage | Format-List *

Get-CimInstance -ClassName Win32_ComputerSystem | Select-Object AutomaticManagedPagefile
Get-CimInstance -ClassName Win32_ComputerSystem | Set-CimInstance -Property @{AutomaticManagedPagefile=$true}
Get-CimInstance -ClassName Win32_ComputerSystem | Select-Object AutomaticManagedPagefile

bcdedit /enum '{badmemory}'


To check Windows:

Run tuneup1.bat > post a share link


My Computer My Computer

At a glance

Windows 10Intel(R) Core(TM) i7-4800MQ CPU @ 2.70GHz16 GB Total: Manufacturer : Samsung MemoryTyp...NVIDIA Quadro K3100M; Intel(R) HD Graphics 4600
OS
Windows 10
Computer type
Laptop
Manufacturer/Model
HP
CPU
Intel(R) Core(TM) i7-4800MQ CPU @ 2.70GHz
Motherboard
Product : 190A Version : KBC Version 94.56
Memory
16 GB Total: Manufacturer : Samsung MemoryType : DDR3 FormFactor : SODIMM Capacity : 8GB Speed : 1600
Graphics Card(s)
NVIDIA Quadro K3100M; Intel(R) HD Graphics 4600
Sound Card
IDT High Definition Audio CODEC; PNP Device ID HDAUDIO\FUNC_01&VEN_111D&DEV_76E0
Hard Drives
Model Hitachi HTS727575A9E364
Antivirus
Microsoft Defender
Other Info
Mobile Workstation

Latest Support Threads

Back
Top Bottom